Contact us
Guardian by Cloudhouse | Configuration Drift Detection & Compliance Automation
Cloudhouse Guardian

Control change before it becomes risk, outage, or audit failure.

Guardian gives you continuous visibility across your entire IT estate. It detects configuration drift in real time, reconciles every change against approved baselines, and produces defensible evidence for every auditor, board, and regulator that asks.

Guardian
Drift detected Live
AssetPROD-DB-04
TypeFirewall rule
ApprovalNone found
Change reconciled ServiceNow
CR refCHG0094217
MatchApproved
RiskWithin window
OwnerCAB-validated
Audit evidence Auto
StandardCIS Benchmark
Coverage100%
FrameworksFCA · DORA · SOX
StatusAudit-ready
$14,056
Average cost of IT downtime, per minute. (Gartner)
80%
Of outages caused by configuration change. (Gartner)
50+
Global enterprises trust Guardian to protect their estate
One
Independent view of drift, change and compliance, across the estate
The Problem

IT estates naturally diverge. Unvalidated change is silent risk.

Manual interventions, emergency fixes, and inconsistent governance pull every IT estate away from its approved baseline. Without continuous drift detection and change reconciliation, you are flying blind between audits, exposed to downtime, compliance gaps, and unplanned cost.

The Compliance Pressure Curve
Jan 2025
DORA enters into force
EU financial entities now required to evidence ICT risk management, including configuration controls and change validation.
Now , Apr 2026
NIS2 enforcement deepens
Member states tightening scrutiny on essential and important entities. Senior management held personally accountable for configuration and change failures.
Ongoing
FCA, SOX, GDPR, ISO 27001
Continuous configuration evidence demanded across financial services, listed companies, data controllers, and certified estates.
Every audit
The same question
"Show us what changed, when, by whom, against which approval." Without Guardian, that answer takes weeks. With Guardian, minutes.

Drift is silent. Outages are loud. Audits are unforgiving.

Eighty per cent of outages are caused by configuration change. Yet most enterprises still rely on point-in-time scans, ticket queues and tribal knowledge to govern change. The gap between what was approved and what is actually running is where risk lives.

Manual reconciliation doesn't scale. Spreadsheet evidence doesn't satisfy auditors. And in a regulatory environment where directors are now personally accountable, "we think it's fine" is no longer an acceptable answer.

01

Silent configuration drift

Baselines erode over time. Manual fixes, emergency patches and out-of-process edits accumulate quietly until something breaks, or an auditor asks.

02

Unapproved change goes unseen

Without reconciliation against ServiceNow, FreshService or your CMDB, approved and unapproved change look identical. You cannot govern what you cannot see.

03

Audit fire-drills cost weeks

FCA, SOX, DORA, NIS2, GDPR, every auditor wants the same evidence. Without continuous compliance, every audit is a scramble of screenshots and spreadsheets.

How Guardian Works

One continuous loop. From baseline to evidence.

Guardian deploys lightweight collectors across your estate, establishes a known-good baseline, and monitors every configuration element from that moment on. Change is reconciled against your change management system. Deviations are flagged. Evidence is ready whenever you need it.

Step 01

Baseline

Scan every layer of your estate. Servers, end-user computing, networks, on-prem, cloud, container. Establish a single, known-good configuration baseline.

Step 02

Detect

Continuously monitor for configuration change at forensic level. Know exactly what changed, when, and by whom, anywhere in the estate.

Step 03

Reconcile

Match every detected change to its Change Request in ServiceNow, FreshService, Ivanti Neurons or BMC Helix. Approved and unapproved, separated in real time.

Step 04

Evidence

Automate assessment against CIS Benchmarks and bespoke policies. Generate on-demand evidence for FCA, SOX, DORA, NIS2 and GDPR.

What Guardian delivers
Forensic-level drift tracking
Change reconciliation
Embedded CIS Benchmarks
ServiceNow, FreshService, BMC, Ivanti
On-prem, hybrid, any cloud
FCA, SOX, DORA, NIS2, GDPR ready
Audit-ready evidence on demand
See Guardian

What your team will actually see.

The state of the estate, what failed, and how to fix it. Screens from a Guardian environment.

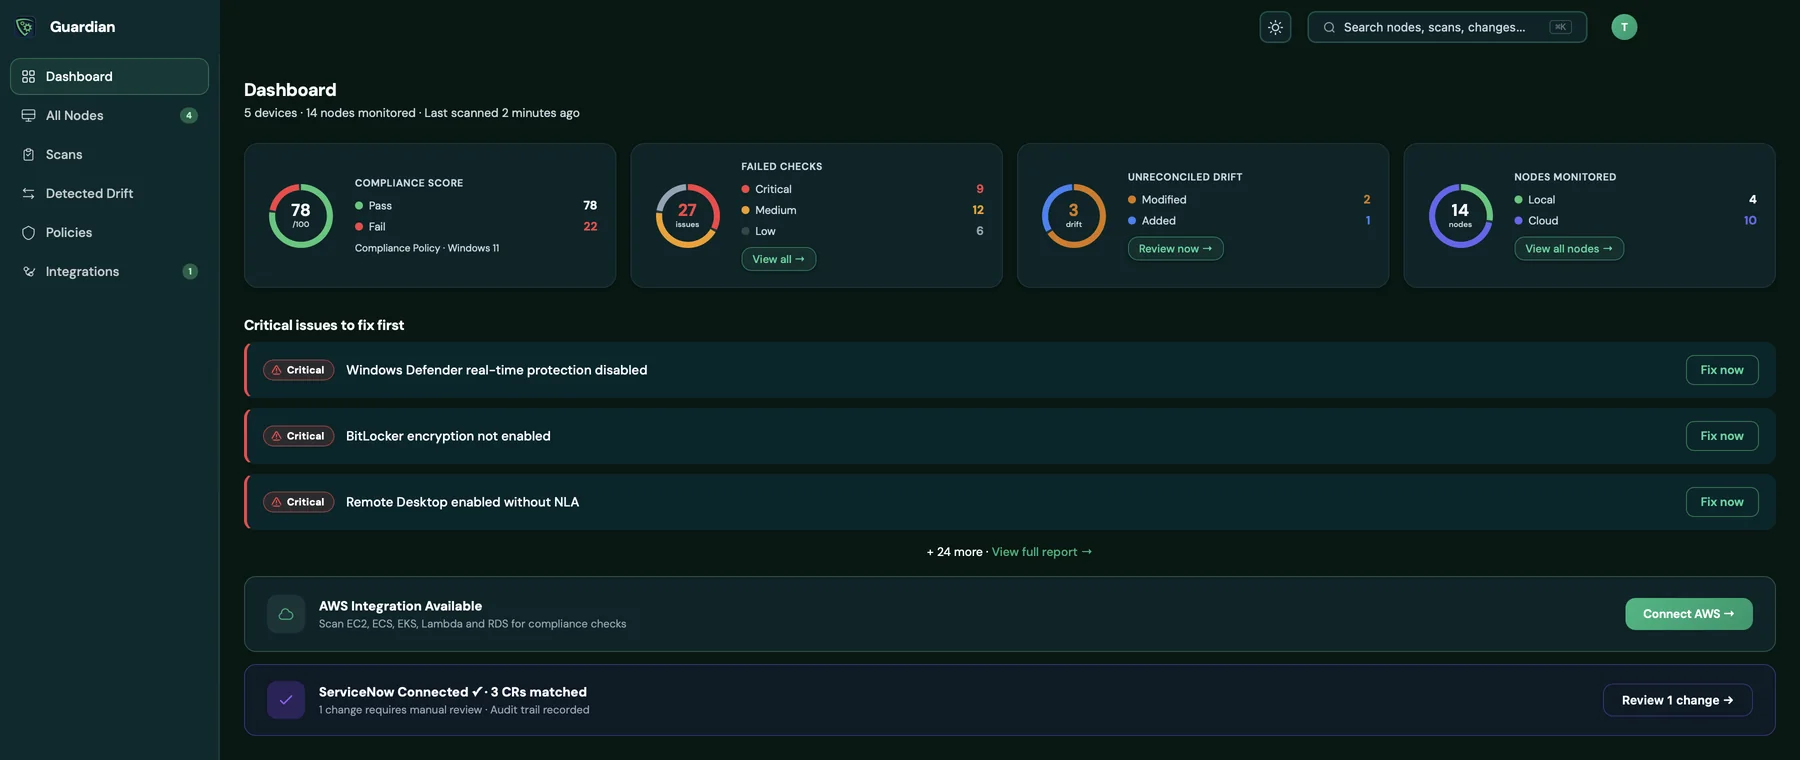
Guardian dashboard showing a compliance score of 78 out of 100, 27 failed checks by severity, 3 unreconciled drift items, 14 nodes monitored across local and cloud, critical issues to fix first, and ServiceNow connected with 3 change requests matched.
One view of the estate. Compliance score, failed checks by severity, unreconciled drift and every node monitored, local and cloud. Detected changes are matched to ServiceNow change requests, and anything that needs a human is queued for review.
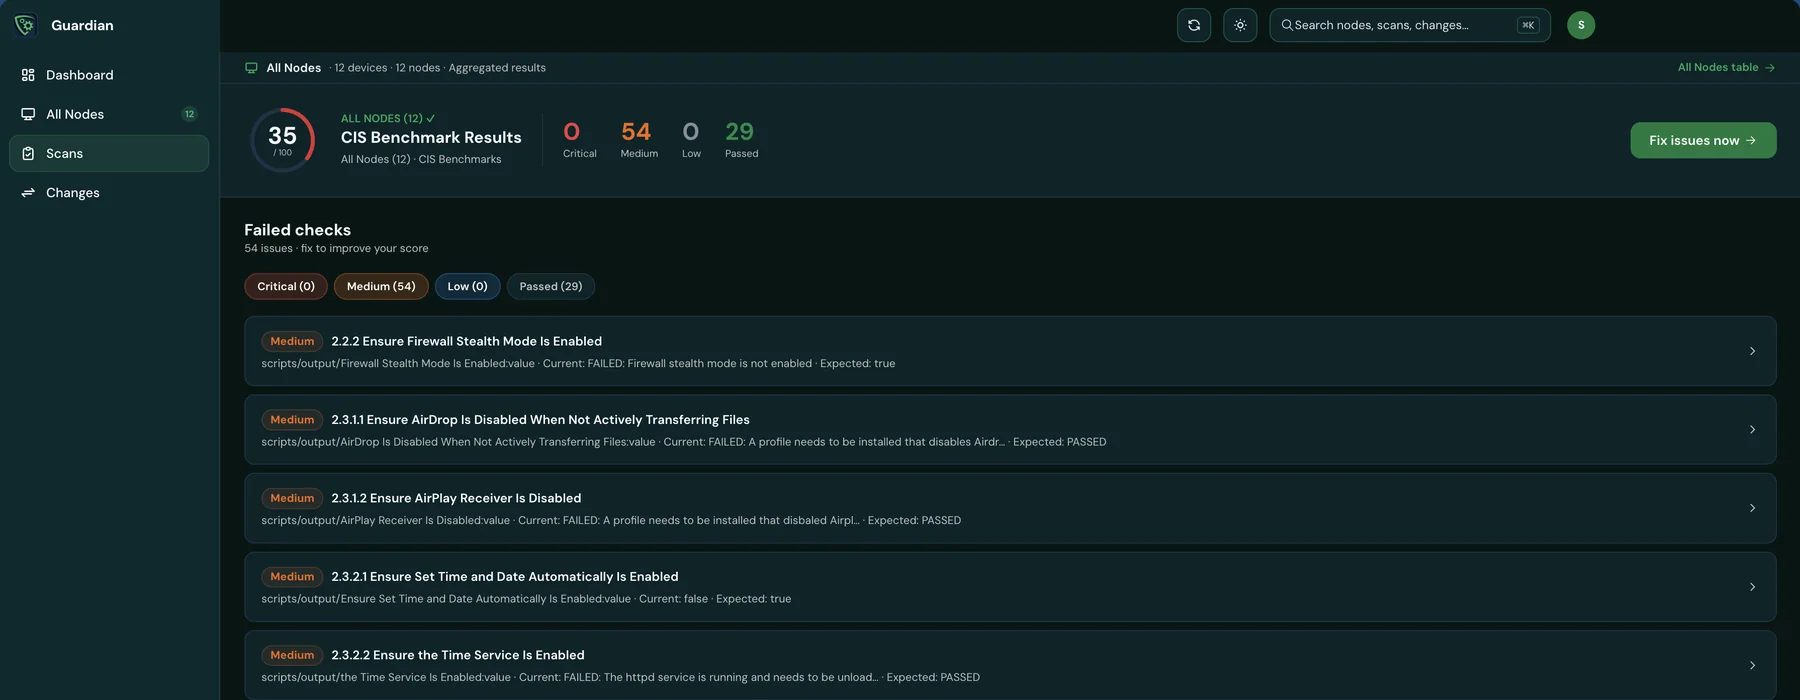
Guardian CIS Benchmark results aggregated across 12 nodes, listing each failed check with its CIS reference, the current value found and the expected value.
CIS Benchmarks, check by check. Results aggregated across every node, with the CIS reference, the value Guardian found and the value it expected.
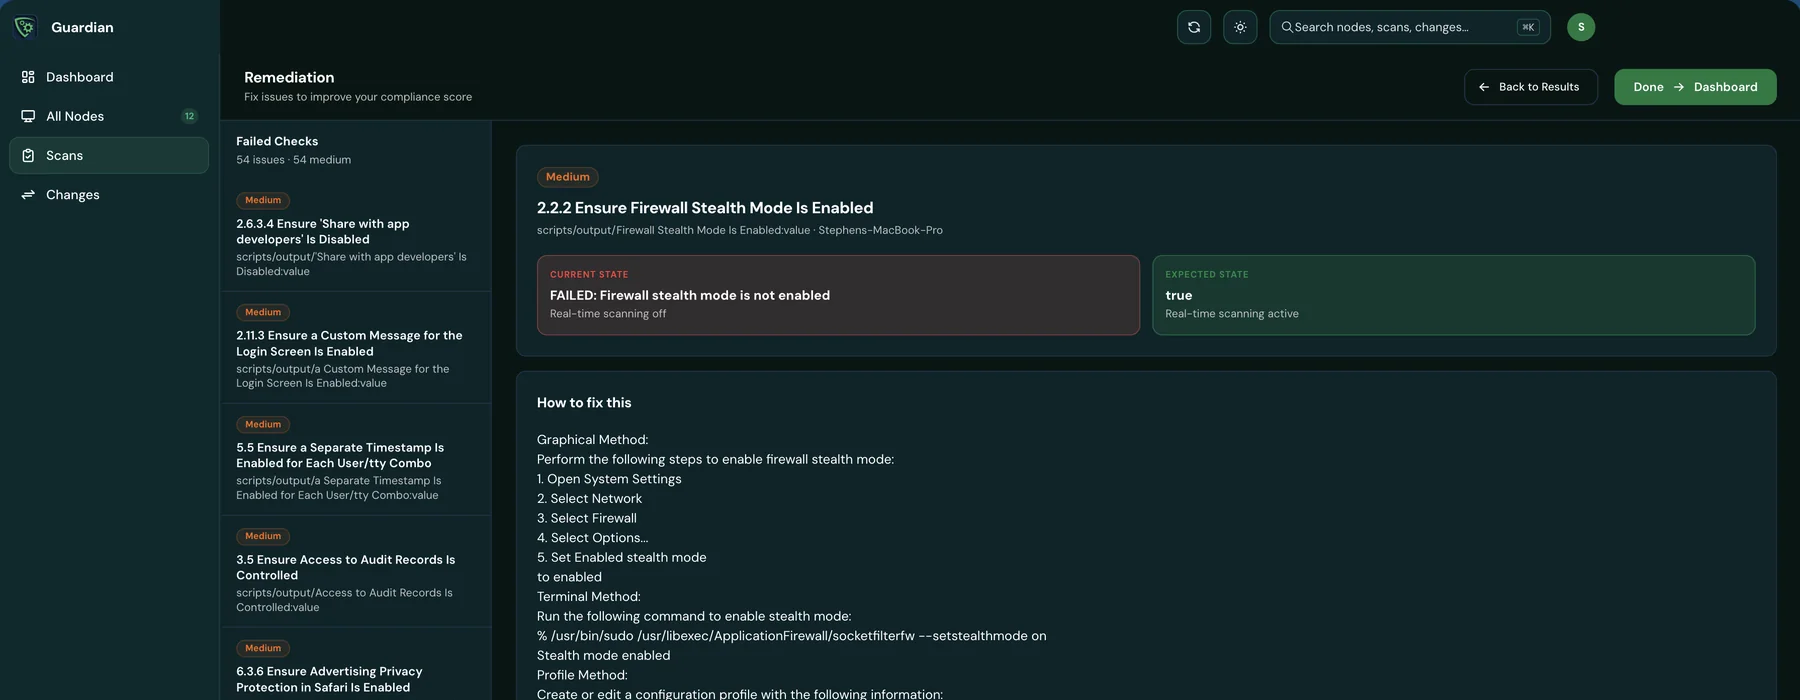
Guardian remediation view for a failed CIS check, showing current state against expected state and step-by-step instructions to fix it.
From finding to fix. Current state against expected state, step-by-step remediation, then a rescan to prove the fix or a recorded risk acceptance.
Use Cases

Three jobs. One independent view.

Whether you are reporting to regulators, validating a change programme, or proving compliance against a published standard, Guardian gives you the same defensible evidence, generated continuously and exported on demand.

Compliance Reporting

Prove compliance to regulators

Continuous evidence against CIS Benchmarks, FCA, SOX, DORA, NIS2 and GDPR. Replace pre-audit fire-drills and manual screenshots with detailed, exportable proof, generated automatically.

300+
pages of mandated configuration validated automatically (Bangor Savings Bank)
Start a Guardian trial
Process Improvement

Validate every change, in real time

Reconcile detected change against ServiceNow, FreshService, Ivanti Neurons or BMC Helix. Surface unapproved or out-of-window change instantly. Strengthen CAB governance with hard evidence, not opinion.

Real-time
approved vs unapproved change, exposed automatically
Explore the platform
Validation Automation

Cut MTR. Protect the SLA.

When something breaks, the first question is always the same, what changed? Guardian gives operations teams forensic change detail to identify the likely cause and remediate before incidents escalate.

Minutes
to root cause, instead of hours of triage
Talk to our team
Any Environment. One Truth.

From on-prem to container, Guardian sees it all.

Drift does not respect infrastructure boundaries. Guardian provides unified visibility and governance across every layer of your estate, on-prem, cloud, or hybrid, so the same policies, the same evidence, and the same standards apply everywhere.

On-Prem

Restore control over complex on-prem estates. Manual interventions, emergency fixes and inconsistent governance all surface, continuously.

Any Cloud

Replace the cloud wild west with controlled, auditable operations. Policy-driven automation keeps drift, cost and compliance risk in check.

Hybrid

Unify governance across servers, clouds and Kubernetes. One set of policies, one evidence trail, across every layer, every speed.

Automated evidence against your compliance obligations
NIS2
DORA
FCA
SOX
GDPR
CIS BENCHMARKS
What It Unlocks

More than monitoring. Defensible governance.

Guardian doesn't just detect drift. It restores the audit trail your governance has been missing, across every layer of the estate, every speed of change, every standard you are held to.

For the CIO

Face auditors with evidence, not explanations

Defensible audit trails covering every configuration change, every approval status, every compliance assessment. Export the proof directly, no spreadsheet rebuild required.

300+
pages of mandated configuration validated automatically
For Operations

Prevent outages, don't just react to them

Eighty per cent of outages are caused by configuration change. Surface anomalies before they escalate. Keep critical systems within their approved configuration envelope.

80%
of outages traced to configuration change (Gartner)
For the Estate

Unify governance across on-prem, cloud and container

One policy set, one evidence trail, one independent view. From mainframe to Kubernetes, from FCA to NIS2, the same standards applied everywhere.

One
truth, every layer, every speed of change
For the Team

Restore trust in change

Move from "we think it's fine" to "we can prove it." Give CIOs, CISOs and IT Directors the same single source of truth, with no finger-pointing between teams.

Zero
finger-pointing. One independent view, agreed by all
Inside Guardian

Four capabilities. One job: keeping change under control.

Everything Guardian does ladders up to one outcome, controlling change before it becomes risk, outage or audit failure. Here is what sits under the hood.

Continuous Drift Detection

Monitor your entire IT estate for configuration change in real time. Forensic-level tracking across servers, end-user computing, networks, on-prem, cloud and container. Anomalies surfaced before they escalate.

Change Reconciliation

Integrations with ServiceNow, FreshService, Ivanti Neurons and BMC Helix link every detected change to its Change Request. Approved vs unapproved change, exposed in real time, no manual reconciliation.

Compliance Automation

Embedded CIS Benchmarks plus bespoke Guardian Policies run continuously against your estate. Generate detailed evidence for FCA, SOX, DORA, NIS and GDPR without the spreadsheet fire-drill.

Audit-Ready Reporting

Track, visualise and improve change governance with clear, auditable trails. Know exactly what changed, when, and by whom, and export defensible evidence on demand for every regulator that asks.

Trusted where change cannot fail

50+ Enterprises · NYSE · Amadeus · Akamai · Bangor · Ascensus · SCU
NYSE
Amadeus
Akamai
Bangor Savings Bank
Ascensus
SCU
Customer Voices

From flying blind to fully accountable.

Real outcomes from organisations using Guardian to govern change at scale.

Guardian gives us unparalleled visibility into our environment. Regulators often ask how we ensure compliance, and with Guardian, we can confidently prove it. The time savings and improved oversight have been game-changing.

BS
Bangor Savings Bank
Financial Services , United States

Guardian replaced manual checks across 300+ pages of mandated configuration that were degrading our IT capacity. We now have continuous evidence, not point-in-time snapshots, which has fundamentally changed how we approach audit.

FS
A Major US Financial Services Customer
Compliance & Risk , Configuration Governance
Technical Capabilities

One platform for the full change lifecycle.

From first detection to defensible evidence, every capability sits inside Guardian. Click any to expand.

Guardian's drift engine compares configurations over time at forensic level. Track every attribute and configuration element, from servers and end-user computing through to network infrastructure, on-prem, cloud, hybrid and containerised environments. Anomalies are surfaced before they escalate into incidents.

Out-of-the-box integration with ServiceNow, FreshService, Ivanti Neurons and BMC Helix. Every detected change is matched to its approved Change Request automatically, exposing approved versus unapproved deviation in real time. Audit thoroughly. Evidence strict adherence to change management policy organisation-wide.

Guardian ships with embedded CIS Benchmarks and supports bespoke Guardian Policies tailored to your environment. Continuous compliance monitoring against industry-recognised standards, with detailed evidence generated automatically.

Track, visualise and improve change governance with clear, auditable trails. Know exactly what changed, when, and by whom. Export defensible evidence on demand for FCA, SOX, DORA, NIS2 and GDPR.

Unified governance across on-premise infrastructure, AWS, Azure, GCP and any other cloud, plus container ecosystems including Kubernetes. One set of policies, one evidence trail, every layer.

Reduce mean time to resolution with detailed change information that highlights the likely cause and supports rapid remediation before incidents escalate. Replace tribal knowledge and chat-thread archaeology with a single, searchable record of truth.

Guardian sits outside your existing tooling, providing an independent, verifiable view of your technology landscape. The result is confident decision-making for CIOs, CISOs and IT Directors, all looking at the same single source of truth.

A fully functional Guardian trial. Scan your own estate or use our demo data. See live drift detection, the first reconciled change, and your first compliance evidence within minutes of deployment. No credit card required.

Evaluating alternatives?

See how Guardian compares with other drift detection tools

A side-by-side comparison with Tripwire, Netwrix Change Tracker, Evolven, CimTrak, Wiz and IaC drift tools.

Compare Guardian
Stop Flying Blind

Your auditor is coming.
Your evidence is ready.

Take Guardian for a test drive. A fully functional trial, your estate or our demo data. See live drift, first reconciliation and first compliance evidence within minutes of deploy.