In the public sector, cyber resilience comes with scrutiny. Yet maintaining control across vast and complex IT estates is increasingly difficult. The Government Cyber Action Plan estimates that 28% of the government technology estate is legacy technology, leaving a significant proportion of systems particularly vulnerable to attack.
Government departments, local authorities and other public bodies need to know what is happening across their IT estate, demonstrate that changes are controlled and provide evidence that systems are configured securely.
That becomes harder when estates span thousands of devices, multiple teams, departments and arm’s-length bodies. A configuration can change through a routine patch, an approved update or activity carried out by another team. The challenge is not simply spotting that something changed. It is knowing whether that change was authorised and whether the system remains in the state it should be.
Knowing your estate is only the start
The UK Government is placing greater emphasis on visibility and assurance. GovAssure uses the NCSC Cyber Assessment Framework to assess government organisations’ cyber resilience, while Secure by Design and Cyber Essentials form part of the wider approach to strengthening security across the public sector. While these initiatives play different roles, they reinforce a common requirement: organisations need to understand their estate and have the evidence to demonstrate change.
Guardian by Cloudhouse is a configuration monitoring platform. It establishes a trusted baseline across the estate and continuously monitors for configuration drift, giving organisations visibility of how systems are configured and how they change over time. It also measures systems against CIS benchmarks, helping teams evidence their security baseline rather than simply assuming systems remain configured as intended.
For larger and more distributed estates, Guardian can segment systems by department, agency or team, allowing administration to be delegated while maintaining a central view across the organisation.
Proving change is under control
Estate-wide visibility only gets you so far. Public-sector organisations also need to understand what changed and whether it was authorised.
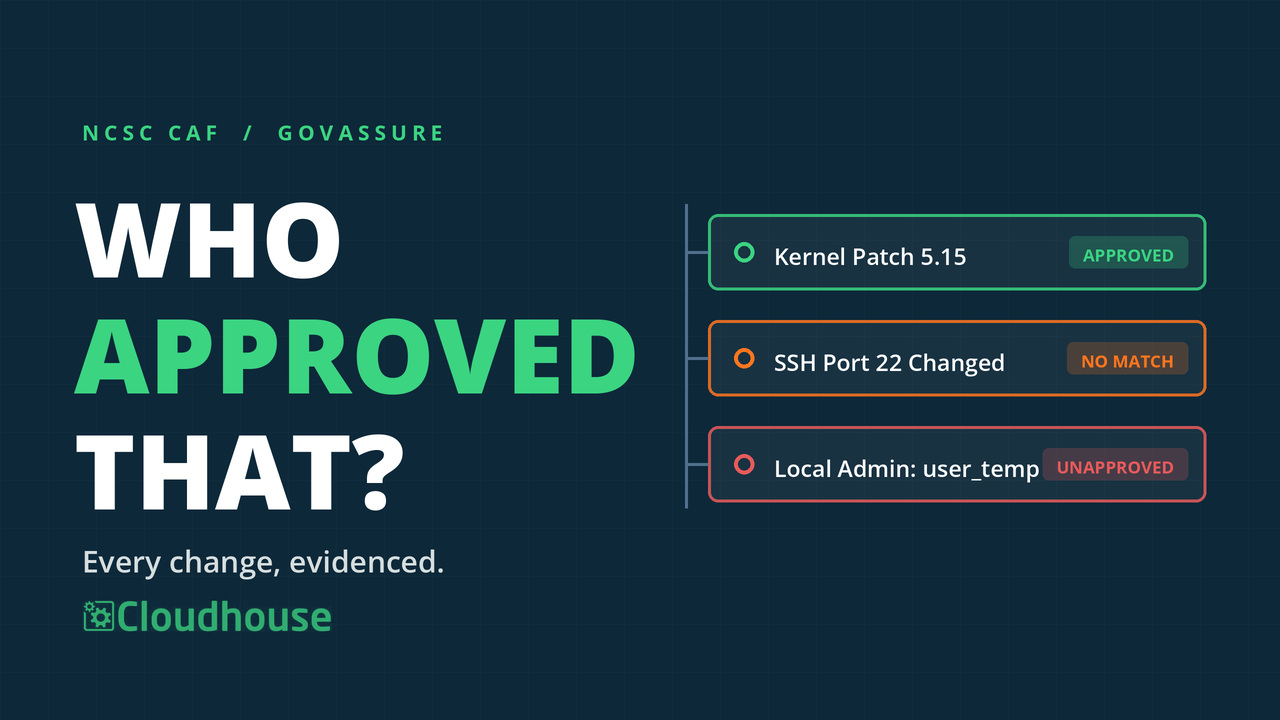
Guardian reconciles detected configuration changes against approved change records, identifying them as matched, unmatched or ambiguous. Expected activity can be separated from exceptions that need investigation, helping teams identify unexpected change as it happens rather than discovering it later.
Every detection, reconciliation and subsequent action is captured in a durable audit trail. Instead of piecing together evidence when an assessment begins, teams have a continuous record of change. Consider an assessor asking about a configuration change made six months ago. Without that record, answering can mean searching through tickets, spreadsheets and different systems to reconstruct what happened. With Guardian, the evidence is already there.
For public-sector organisations facing growing expectations around cyber resilience and assurance, that matters. Knowing your estate is important. Being able to demonstrate that systems are securely configured, change is controlled and exceptions are identified is what turns visibility into assurance.
Watch the video below to see how Guardian helps public-sector organisations know their estate, control change and prove it.